×
Site Menu
Everything
International
Tenders
Local
Finance
Technology
ClickFix Attacks Evolve to Better Hide Malicious Payloads
4 days ago
36
Threat actors are now hiding payloads by using DNS TXT records and browser cache pre-fetching, making it tougher to spot early attack stages.
Read Entire Article
Homepage
International
ClickFix Attacks Evolve to Better Hide Malicious Payloads
Related
FBI Arrests Founder of Ransomware Negotiation Firm
1 day ago
18
ASOS Breach Reveals the Risks in Customer-Facing SaaS
1 day ago
17
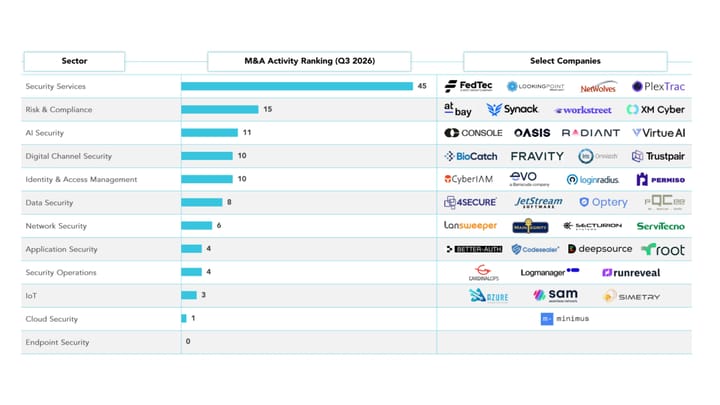
AI Scramble Drives Cybersecurity M&A Boom
1 day ago
17
What We Missed: FBI Strikes Back at ShinyHunters
1 day ago
18
Security Threats Don't Stop at the Office: Why Executives' F...
1 day ago
18
$10 million bounty offered for Chinese Hafnium hacker accuse...
1 day ago
21
Social Engineering AI Agents: The New BEC for 2026
1 day ago
22
'AgentCorruption' Puts AWS Environments At Risk With Single ...
2 days ago
31
Venezuelan Cartel's Malware Honcho Nabbed for ATM Jackpottin...
2 days ago
27
Russian Spies Give 'MatchBoil' Malware a Stealthy Facelift
2 days ago
35
Everything
International
Tenders
Local
Finance
Technology

.jpg)


.jpeg)